Showing posts with label Azure cloud. Show all posts

Thursday, May 23, 2019

Cloud Native way of security


How to secure cloud in cloud native era

Introduction
When it comes to cloud security there are approaches that rely on same tools that worked for on premise infrastructure. Those approaches are commonly referred as on premise security posture. We are seeing that more companies are making cloud native applications. For cloud security, there is a need to have a shift from on premise security posture to a cloud native approach to security. We need to take an approach that relies more on native cloud primitives offered by the cloud provider.

Cloud native way of security
Cloud infrastructure has become the de facto infrastructure for hosting applications and workloads that enable a business to provide value. Cloud has proved to be a value multiplier and more and more businesses are trying to tap into the cloud value. In terms of the applications, companies are shifting to cloud native approach for application architecture. This shift towards cloud native applications is the right approach as this helps companies realize the cloud value. The cloud native way of security is taking the cloud native approach for the applications and applying it for cloud security. For example, the cloud native application is architected to use cloud platform as a resource and not just a hosting environment, similarly cloud native security is tapping into cloud platform for providing security posture.
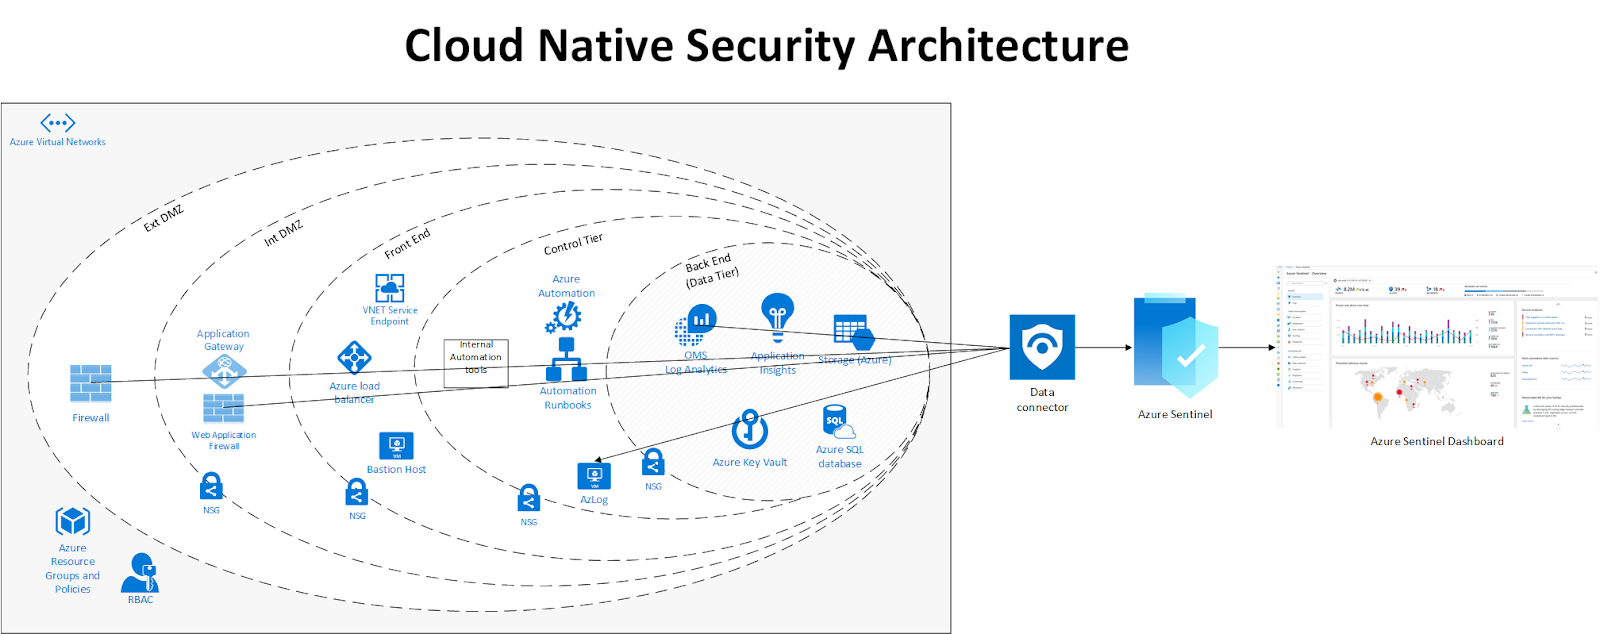
Note: The left side of the cloud native security shots the conceptual view of security in depth. The implementation architecture might show each layer as a separate entity at the same level.

Why we need Cloud native way of security
It is all about the understanding and the approach that is the result of the understanding. There are two mindsets when it comes to cloud security. One mindset is about looking at what has worked at on premise data center and replicating it to cloud. The other mindset is looking at cloud as a platform for resources that provides components for cloud security. The on premise mindset typically involves looking the resources as virtual machines that are part of a network and are joined to a domain. The security tools that have evolved over the years for on premise resources essentially addresses the same scheme. These security tools involve (and not limited to):

  •       Relying on host operating systems to provide security by managing and restricting incoming and outgoing traffic flow to/from ports. A good example is a windows firewall. 
  •       Recording all the traffic that is flowing in and out of the network and then analyzing the traffic to flag any suspicious traffic flow. This also give us idea that security actions are typically thought of as reactive action and not proactive actions.
The above two points are just the two examples of security tools that are employed by on premise approach. The intention here is to point out the mindset where security is delegated to tools and not built in the resources/workloads that are part of an on premise establishment.
The reason that those tools were designed that way was because the cloud providers did not offered alternatives to support the cloud native mindset. If we go back a couple of years ago and image that we had to host a cloud native application, we still had to rely on the tools that worked before.
Now the time has changed. The cloud providers have addressed the lack of security tools as part of the cloud infrastructure. We have entered an era where native cloud security tools or cloud primitive tools have evolved to fully support the cloud native security. The need is to create cloud based solution architectures that leverage the cloud primitive security capabilities. For example:
·       Instead of relying on windows firewall, NSG (in case of Azure) should be employed. That will also mean to evolve the network architectures that designed for clouds to support that. 
·       Instead of using security tools that record all the traffic, tools like Azure Sentinel should be employed.


Case for Cloud native way of security
Shift-Left Security: With the cloud native way of security approach there will be more push towards achieving security using the shift-left approach. This means that instead of security being addressed something as wrapper, it will be addressed as a feature that is "baked in" into the architecture from the beginning. That is the very definition of the Shift-Left approach.
Security by platform: As more and more systems are being automated and moved to cloud, more and more threats are emerging. The threats are becoming multidimensional in nature. The cloud-native way of security is better equipped to cope with the present and emergent threats.
Defense in Depth: Cloud native way of security allows multiple mitigations applied against threats. If we replace the cloud native way of security with on premise way of security, then we would need to have multiple layers of security that we have to stand up and maintain either by ourselves or the vendors.
Scale: Cloud native way of security is platform based, so it inherently scales within the platform. To understand this, imagine we are back in 2000s. The data that was being generated at that time was not much in scale what we have now. For that time the on premise infrastructure was provisioned to cater the needs of that footprint of data. Now we are in an era of “big data” and to support the scale requirement for that enormous amount of data, we would need more dedicated resources.
Focus on business value: With Cloud native way of security, the focus of business is shifted from security and business to only business. This also means that the computing base that a business is responsible for has been reduce. This makes the systems more secure as there is less computing base that a business needs to protect.
Containerization (aka Kubernetes) revolution: With the advent of containerization more and more applications have shifted towards cloud native architecture. This shift means that the classical cloud security model needs a shift as well towards cloud native way of security.


Example Components of Cloud Native Security Architecture
Azure Sentinel
Each cloud provider has developed its own set of tools that can be defined in the realm of cloud native way of security. From Azure’s side, the tool that implements the cloud native way of security is “Azure Sentinel”. Azure Sentinel is a cloud-native SEIM that leverages AI for threat protection. The way Azure Sentinel works is that it uses Data Connectors. The Data Connectors hook into various Azure services such as Firewall. The Data Connectors then feed in data to Azure Sentinel. Azure Sentinel runs the security related tasks and then shows the security landscape onto a dashboard. More information on Azure Sentinel can be found here.

DDoS Protection
This is a platform level service that Azure offers. As mentioned earlier, the cloud providers are now answering to the call of providing cloud native security tools. Azure DDoS is one of the newer service that helps against the DDoS targeting cloud resources.

Firewalls
Firewalls is an Azure service that helps protect the virtual networks. Since it is a managed service offering there are advantages that come with it. These advantages include real time analysis of traffic and then feeding in the data to Azure Sentinel.

Web Application Firewall
For the applications that are hosted on Azure App services, the web application firewall is essential for it security. For a truly cloud native application that is hosted on App service, just adding the Web Application Firewall will make it cloud native for security.

Azure NSG
NSG is a primitive (native) service offering that helps us implement traffic rules for incoming and outgoing traffic. The beauty of NSG is that it acts like windows firewall but can be applied to various resources such as subnet. In case of subnet if NSG is added then the NSG rules will be enforced on all the VMs and other resources that are part of that particular subnet.

Conclusion
In this article we have looked at the two approaches to cloud security. As we have seen from the tools and the conceptual architecture there are Managed Services that are offered by the cloud providers. Using Managed Services for cloud security infrastructure is the step in the right direction to achieve cloud-native security.

Wednesday, January 23, 2019

Presentation - Architecting Solutions for Azure

This is probably my shorts blog post. Recently I had the honor to present at San Diego .NET user group. I really enjoyed presenting there.  The audience was amazing.

Here is the link to the presentation:


Presentation - Architecting Solutions for Azure

Thursday, November 1, 2018

Getting started with Azure Sphere

Azure Sphere - MT 3620 on my work desk


Note: This is first of a series of blog posts that are related to my work done on Azure Sphere. Stay tuned for more on Azure Sphere.

Introduction

One of the best to learn a new technology is to just get hands dirty start work on the new technology. In this blog,  I will take you through the steps that I carried out in order to start work on Azure Sphere.

Once you have received the Azure Sphere device, it's time to get started. Here is the link https://azure.microsoft.com/en-us/services/azure-sphere/get-started/that will take you through the steps of acquiring a Azure Sphere device.

1. The very step is to attached the device with your development machine. If you have the correct operating system then the device manager should automatically install the drivers. In my case the drivers for the device did not install automatically so I had to go to a special page that allowed me to download the drivers. Visit http://www.ftdichip.com/Drivers/VCP.htm to download the driver. The following image shows the driver that I downloaded for my development machine:


2. Once you downloaded and install the drivers, your device manager should look like as the following image.


Notice the three USB Serial Ports (in my case I got COM 4, COM 6 and COM 7)


3. Download Install Azure Sphere SDK for Visual Studio Preview.

4. The Azure Sphere SDK for Visual Studio Preview would install the Azure Sphere Developer Command Prompt Preview. This command line utility is your bridge between the Azure Sphere device and your development effort.

5. Run azsphere login command on  "Azure Sphere Developer Command Prompt Preview" to ensure you can Azure Sphere SDK has been properly installed and you can access your subscription.

6. Creating a Tenant
azsphere tenant create --name mytenant

0000000-xxxx-xxxx-xxxxx-xxxxxxxxxx mytenant


7. Claiming the device
azsphere device claim

Claiming device.
Successfully claimed device ID 'XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX' into tenant 'afrinish' with ID '0000000-xxxx-xxxx-xxxxx-xxxxxxxxxx'.
Command completed successfully in 00:00:03.3873192.


8. Configure Wi-Fi

azsphere device wifi add --ssid [[yourSSID]] --key [[yourNetworkKey]]

Running the command would yield the following output.

Add network succeeded:
ID                  : 0
SSID                : XXXXXXXXXX
Configuration state : enabled
Connection state    : unknown
Security state      : psk

Command completed successfully in 00:00:02.0253617.


Conclusion

In this blogpost, we have gone through the steps of getting started with Azure Sphere. We started off by acquiring the device, installing necessary software and drivers, configuring the device and connecting it the Wi-Fi. If there any any issues, please use the comments section to ask questions.

The next step would be to start developing. Happy coding!

Tuesday, September 4, 2018

Multi-cloud Architectures for Applications

Multi-cloud architecture for distributed application

Back story

Companies are embracing cloud as part of their key business strategy. Huge part of this embrace is moving their applications to cloud. This created a challenge for major cloud providers, like Amazon, Microsoft and Google, to offer a slew of services that would help companies move to cloud. That brought us to era of cloud architectures. Huge progresswas made (and still is being made) in this area.

As progress was being made in moving to cloud, a risk emerged called “vendor lock-in”. This essentially meant that when the applications where being moved (or even when new applications where being created), the architecture was focused on the services that were provided by on cloud one cloud vender. This is critical because this makes the consumers of applications more vulnerable to dependencies. This was not the only risk that emerged but this was the most significant
and attention.

To remedy that “Multi-cloud” or “Portable” architecture was embraced. Applications were architected in such a way that they could be ported from one cloud provider to another without any major rewrites. New technologies like Kubernetes, Docker and services orchestration technologies went along way to provide underlying technologies to mitigate the “vendorlock-in” risk.

What is Distributed Application Multi-Cloud architecture?

The multi-cloud architectures were great in providing resiliency and removing underlying dependencies which would have locked in to a particular vendor. This made solutions architects to focus on treating their solution as one big entity deployed in redundant fashion. It took focus away from actual application architecture and its nitty gritty details that would have been leveraged by cloud.

“The basic idea of Distributed applications multi-cloud architecture is to architect a solution that is leveraged to the max by cloud and not bounded by the offerings of a cloud provider”.

Every application, albeit micro service or not, is made of constituent components, services or layers. In Distributed Application Multi-Cloud architecture, the architects focus on application’s different components and treat them as components, services or layers that can be deployed to any cloud to gain the maximum benefits.

Advantages of Distributed Application Multi-Cloud architecture

As stated earlier, Distributed Application Multi-Cloud architecture is the evolutionary form of Multi-Cloud architecture, it carries all the advantages of Multi-Cloud architecture. In addition to those advantages, Distributed Application Multi-Cloud architecture offers following advantages:

1. Extra layer of robustness: Since the focus is on the on application’s different constituent components/layers/services, the architecture achieves an extra layer of robustness.

2. Best use of resources: Cloud providers (mostly big cloud providers like Amazon, Google and Microsoft), offer different services with their own pricing model. When a service offering comparison is made between these cloud providers, it would be apparent that some services would be cheaper than other cloud service providers and some would be more expensive than other cloud providers. A Distributed Application Multi-Cloud architecture can provide a solution that would take advantage of the difference in pricing model for different services offered by cloud providers to the advantage of the company for which the solution is being architected. This can translate into considerable cost
advantage.

Here is an example:
You have an API that needs to be deployed with access to general public. This API requires a backend storage. It might make sense to use Azure App Service to host the API and use Azure’s blob storage for the backend storage. But hypothetically, it might appear that using Google’s cloud storage product be a cheaper option without sacrificing application performance.

3. Higher level of services statelessness: As the application’s constituent services are distributed to different cloud providers, a higher level is achieved for the constituent services.

Tenants of Distributed Multi-Cloud Applications Architectures

• Distributed multi-cloud application architectures is the concept for architecting solution to achieving maximum advantage by harnessing service offerings from any cloud provider.

• Focus on looking at the Application’s constituent components as separate entities that can be leveraged to achieve maximum benefit.

• Not every cloud architecture would be a good fit for Distributed Applications Multi-Cloud architectures.

Step by step guide

1. Review application architecture. The end result of this step is an in-depth understanding of the application, its behavior and environment.

2. Identify constituent components of the architecture. This step should yield a list of all the constituent components of the architecture that make up the whole architecture. This very important step as if the constituent components are not identified properly then benefits of the multi-cloud would not apparent.

3. For each constituent component, identify components that can be deployed/hosted on cloud. This would yield constituent components that can be moved/hosted on cloud.

4. For each cloud component (constituent components that can be moved/hosted on cloud), identify the cloud component that can be deployed/hosted on multi-clouds.

5. Re-architect the application based on previous step. This step should yield an architecture that is multi-cloud.

6. Go through each component of the multi-cloud architecture and use a decision tree (give below) to identify if that component should leverage multi-cloud or not. At the end of this step, you will have each component identified for multi-cloud or not.

7. Analyze the architecture as a whole for determine if the multi-cloud should be used. The rationale of this step is to see if there is cost/performance/security benefit that would be leveraged using multi-cloud. If there is only one component that can be leveraged using multi-cloud (and produces considerable benefits as one), then it might not make sense to use multi-cloud.

Wednesday, September 14, 2016

Continuous delivery with Azure App Service

Update:

Click here for the SoCalCode camp presentation about this topic.

Introduction


This post would introduce you to continuous delivery pipeline using Azure app services. We would take a use case and implement the steps that we need to take in order to establish a build pipeline.

What is Continuous Delivery?

In simple words “Constantly develop, automatically build and automatically deploy”. This means that as soon as code is checked in a system would automatically build the application and deploy.

Azure App Services

Azure app services is a set of technologies that enable development of cloud centric Web Apps, Mobile Apps, API Apps and Logic Apps. There is a great introduction to App Services presented at: https://azure.microsoft.com/en-us/documentation/articles/app-service-value-prop-what-is/ .


Power of App Services

To understand the power of Azure App Service you have to compare to a classic Web Application with any of the technology such as Azure App Service Web App. In a classic Web App, a web server such as IIS is the main component. The Web App is installed on IIS and the pages are served through IIS to internet audience. This is a typical on premises infrastructure implementation. You are responsible for managing the security, availability, scale and instrumentation. Part of the classic web app infrastructure is the responsibility of not only delivering the web app but maintenance of the web server. This includes the separation of environments such as development site, QA site, UAT site and the production site. Also, since web server maintenance is part of this infrastructure, you have to also think about the actual server where that web server is installed. The environment that server offers greatly effects how the web server would work. This is another layer of responsibility that a web developer has to keep in mind.
With the App Services, the IIS part has been abstracted away. This means that management of web server (for example IIS) is not the focus but the focus is the delivery of web app. As an application developer we can easily create on App and have it hosted in different deployment slots. These deployment slots makes it easy to create environments such as development site, QA site, UAT site and production site for the same web app.


Continuous delivery pipeline for Azure App Service

Since web server and the server hosting the web server is not part of Azure App Service, the establishment of continuous delivery pipeline is very easy to establish.
Our focus for this post is to list the steps and design patterns that we can use to establish the continuous delivery pipeline.
There are three major steps to establishment of continuous delivery pipeline for Azure App service. These are:


Establishment of development slots

Once you have created an Azure Web App, you have to define its deployment slots. Usually the deployment slots are representation of your different environments. For example, in a typical web development effort you would have following environments:

1.      Development: This is the environment that is used by development team to help them develop different aspects of the project. Typically this is referred simply as “dev”.

2.      QA: This environment is used by the QA team to test the web app separate from the development environment. This is great for providing isolation and also to do better validation testing. Typically this is simply referred as “qa”.

3.      UAT: This environment is used by product owners or stake holders to validate different features after the QA has signed off. Again an isolation from dev and QA allows the UAT to test the web app irrespective of the test data that QA has used to valid. Typically this is simply referred as “uat”. Usually a separate database is attached for the UAT environment.

4.      Staging: This sometimes also known as pre-production. Typically is used to validate the build process and once the build is validated, this environment is swapped with production. Usually the staging environment uses the same production database. This allows the swapping from staging to production seamless without any down time. Typically this is simply referred as “staging”.

5.      Production: This is the actual web application that represents the production environment. Typically this is simply referred as “prod”.

The Azure App Service gives each deployment slot a unique URL. This essentially means that each of the deployment slot is a separate web application. Each of the web app URL representation of the environment is used by different team members. Development team members use the dev URL, QA uses the QA URL, and UAT uses the UAT URL for the web app.
Here is an example of different deployment slots for our API web app.


Establishment of branching strategy

There are a lot of different branching strategies that are used in the industry. The branching strategy is designed or sometimes evolved based on respective objectives. One of those objectives is the environment. What it means is that for different environments different braches are established. To simplify let us take the following branching strategy.

Master branch – For Development environment
QA Branch – For QA and UAT environments
Production – For staging environment


Importance of branching strategy means for continuous delivery

Since the main tenant of continuous delivery system is to automatically we build and automatically from a code check in, we have to pay extra attention to where the code check in takes place. If we look at our branching strategy, it would mean that if we check in the code in the master branch then dev environment should be build. If we check in the QA branch then it means that QA and UAT environments would be build. Same goes for the staging environment. This is why your branching strategy should be representative of your build environments. Let us take a typical scenario to explain more:
Joe (Backend developer) completes first part of the story and checks in the code to master branch. This kicks off a fresh “dev” build.
Jessica (Front end developer) completes the second part of the story and checks in the code. This kicks off another fresh “dev” build. Since the second part of the story completes the story. The build manager merges the master branch into QA branch. This kicks off a QA build and a UAT build for both QA and UAT team members.


Establishment of build/publish process

Azure App Service deployment

There are multiple ways to deployment apps on Azure App Service.  There are:

FTP

This is a most direct and classical way of deploying any web app. The major drawback is that this a total manual process. If you need to automate this, you have to write quite complex scripts.

Web Deploy

This tool allows you to directly deploy web apps to azure app service from visual studio. Although you do not have to use FTP for this scenario but you still have to do actual deployment manually.

Kudu

This build engine is used where we want to have automatic build/publish execution when a source code repository is attached. This means that as soon as a check in take place on a branch (established in step 2), the kudu build process would kick in a do the rest.


Code checked-in to repository  >>  Kudu initiates the build >> Kudu publishes the website


Multiple web apps challenge

The above mentioned steps would work great if you have only one web app in your code repository. For example, you have create a dedicated branch for one web app that has one solution file (.sln). The challenge comes in the shape of a scenario where you have multiple web apps and they all share the same code repository. For example, in a typical business application, you might have one web app that serves the pages and one Web Api app that is consumed by the web app. You might have different release pipeline for WebApi and web App. In this scenario the visual studio solution would contain both projects as part of the solution.
To accommodate the scenario of multiple web apps projects in a solution, you have to take some extra steps.

Step 1. Add app setting to your App Service to uniquely identify your app. This is to give Kudu a way to kick start the build and complete the publishing once code has checked in.


Step 2. Add “.deployment” file to the base of your source code repository. The “.deployment” file gives Kudu a starting point to start the deployment process. Here is a sample:


As you can see what the “.deployment” file is asking Kudu to do is just to call deploy.cmd file. We would look at this in next step.

NOTE: 
Before proceeding further it is important to note that following are prerequisites for the next steps:
1. Nodejs: https://nodejs.org/en/
2. azure-cli: https://azure.microsoft.com/en-us/documentation/articles/virtual-machines-command-line-tools/

Step 3. Create deploy.cmd file. This is the file that would tell Kudu how many different web apps or web Api apps are available in your code base that needs to be built as part of continuous integration pipeline. 

Here is an example of deploy.cmd file:


If you look at this file, you would notice that there are three web apps that are mentioned in the code. These are the three projects that are part of same solution file. What this code is doing is checking which App Service has kicked started the build process. This essentially means the branch where the code check in has happened. The SITE_FLAVOR comes very handy here as we use this App setting to identify the application.


After the app service identification, the deploy.cmd is just calling the corresponding individual deployment files. In our examples there we have three different deployment files. Those are:
deploy.customersapi.cmd
deploy.customersweb.cmd
deploy.anotherapi.cmd
In our next step we would see how you create these individual deployment files.


Generating Deploy.customer.cmd

 Step 1:

Assuming that your customerapi’s project file is at c:\sites\CustomerApi\src\CustomerApi.csproj and customerapi’s solution file is at c:\sites\CustomerApi\src\CustomerApi.csproj and c:\sites\CustomerApi\CustomerApplication.sln. Execute the following command using elevated Administrator mode either on command prompt or Powershell prompt. I always prefer PowerShell because of ease use.

azure site deploymentscript --aspWAP c:\sites\CustomerApi\src\CustomerApi.csproj  -s c:\sites\CustomerApi\CustomerApplication.sln


      Step 2:

Running the above command would yield a file called deploy.cmd. Rename file deploy.cmd to deploy.customersapi.cmd.

Step 3:

Repeat steps 1 and 2 for customersweb and anotherapi projects.


Conclusion

Azure App services are set of very powerful technologies that gives a very clear pathway to establish a continuous delivery pipeline.

SocalCode Camp presentation

The following presentation about this topic presented at the 2016 SocalCode camp.